
Decentralised News · Agentic Finance · Decision research
By Heath Muchena · Source review 2026-11-14 · Instrument version 1.0.0
What Matters
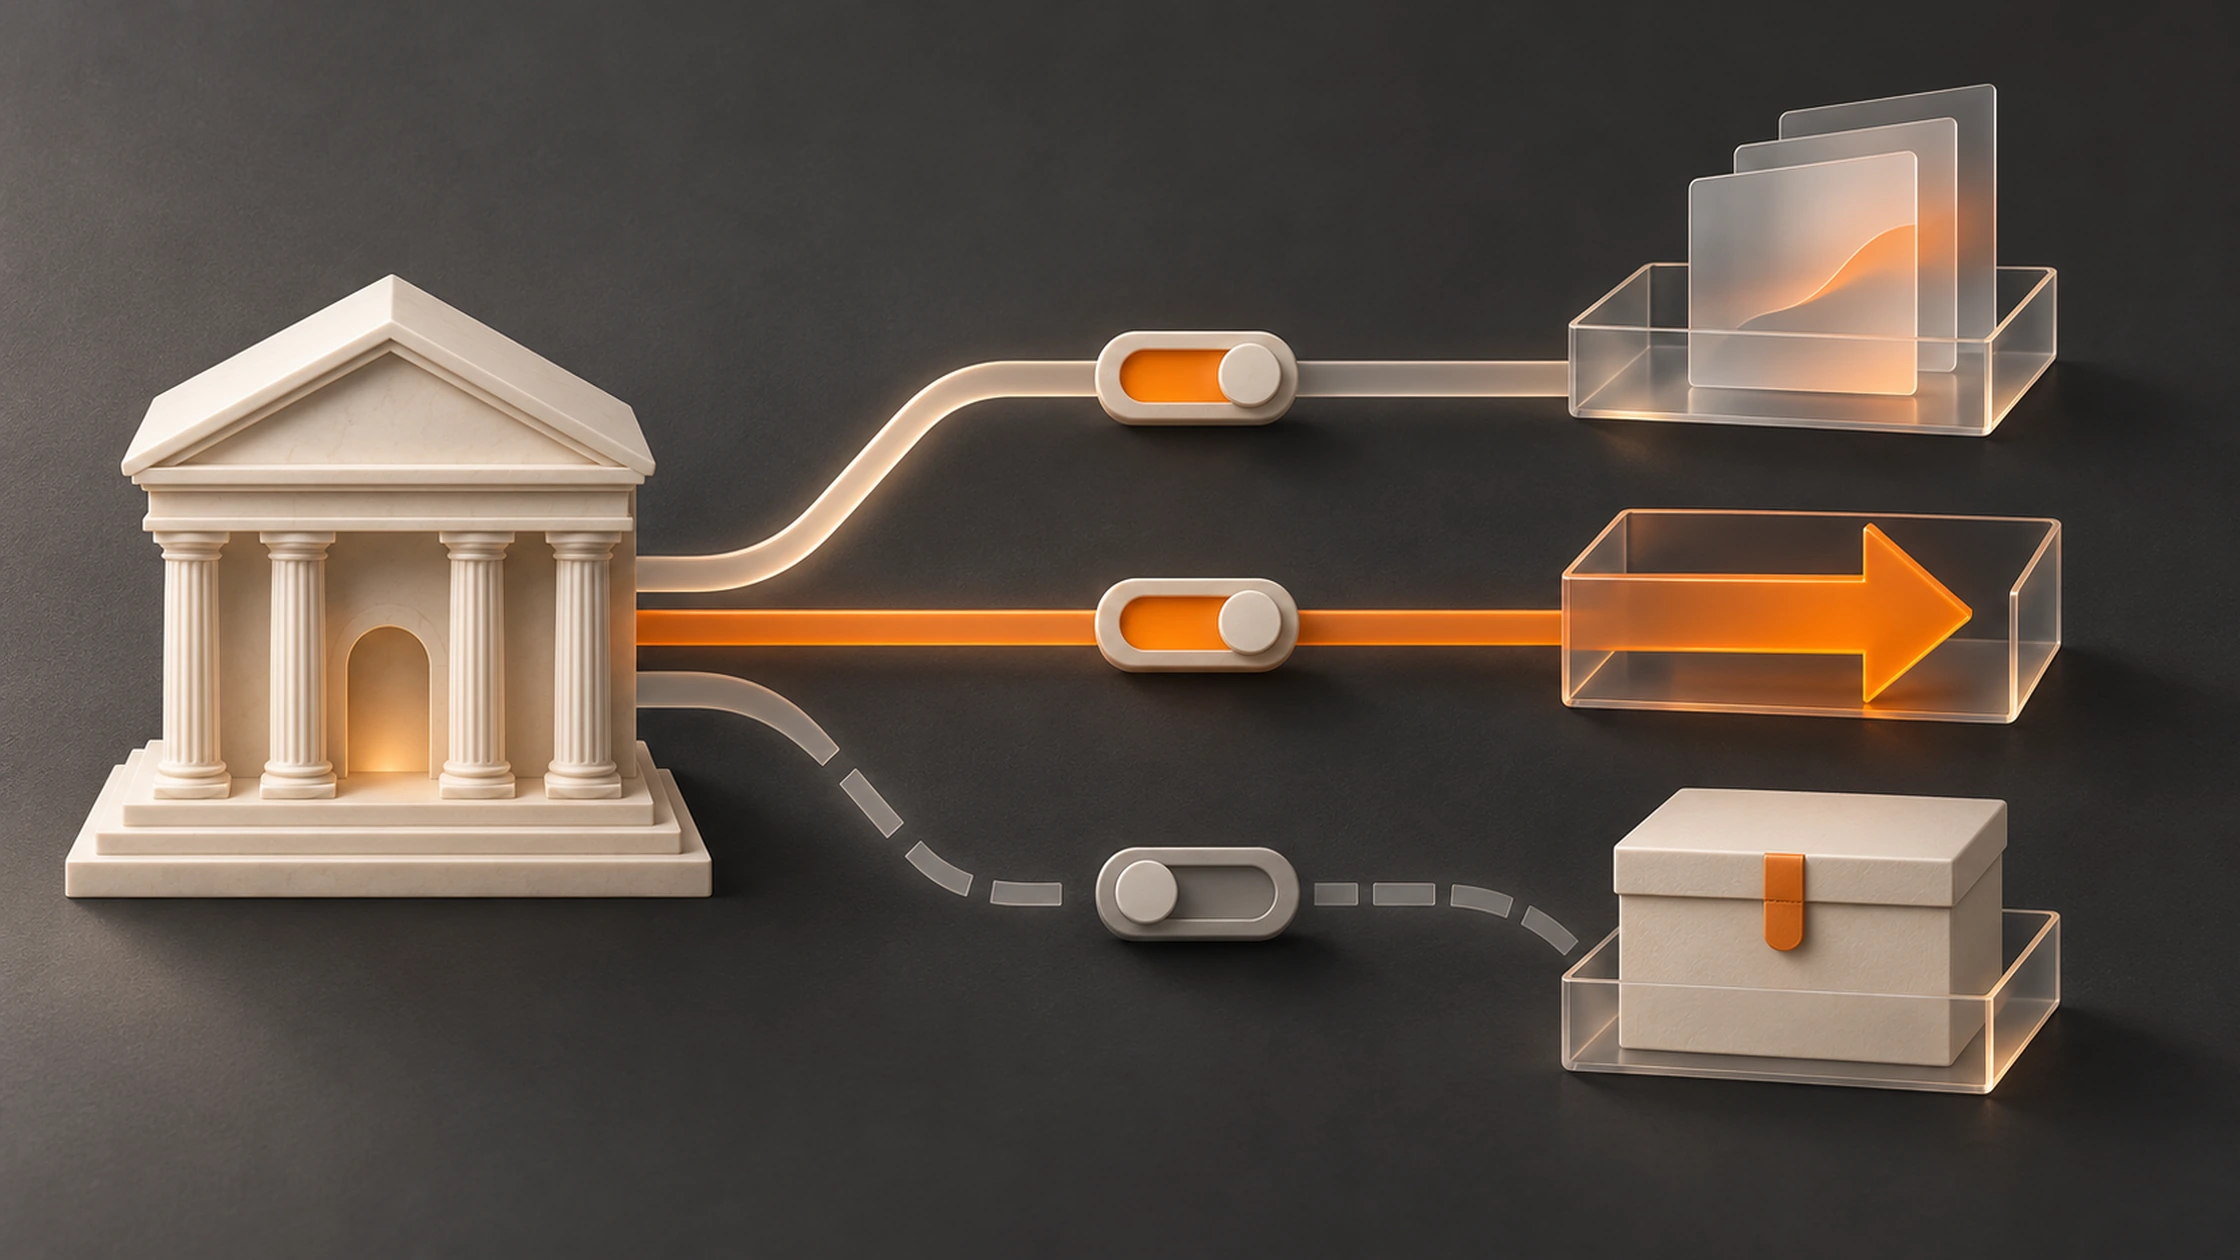
A budgeting task needs a different permission record from a payment task. Withdrawing account-data access does not, by itself, establish cancellation of a payment, removal of a recurring mandate or deletion of copied data.
An assistant asked to explain spending might need account information. An assistant asked to pay a supplier needs a payment workflow. An assistant asked to pay future bills may need a recurring arrangement. Those are different authorizations, even when one application presents them under a single “connect bank” button.
This article uses a UK open-banking scope. The FCA distinguishes account information services (AIS) from payment initiation services (PIS), and requires the relevant explicit consent. Its consumer guidance also asks users to check the firm and its activity permissions. The label “AI agent” does not replace those service roles.
The new DN instrument separates three outcomes that a disconnect screen can obscure: future data access, payment or mandate state, and information already copied. It uses TrueLayer’s explicitly versioned data and payment documentation as examples, not as proof that a particular agent app, bank or customer has a permitted integration. It does not connect an account or verify a consent token.
DN Evidence Block
Sources reviewed: 2026-11-14 · Evidence type: UK regulator and Open Banking guidance plus named TrueLayer technical and privacy documents; original task/scope and state-separation instrument.
Scope: UK payment-account connection decisions. The named technical examples distinguish TrueLayer Data API v1 scopes from Payments API v3 cancellation and mandate behavior. No personal account or agent connector is approved.
- Nine primary sources reviewed on 13 November 2026; article editorial date 14 November.
- The instrument records data access, existing payment, recurring mandate and retained copies independently.
- TrueLayer public documentation is used for the named versions only; sandbox availability, generic branding and a working token do not establish production entitlement.
- ICO erasure guidance currently carries a notice that it is under review following the Data (Use and Access) Act.
Not established by this work: FCA register status of a particular agent app, live bank consent screens, actual scope enforcement, bank compatibility, revocation latency, payment cancellation success, model-provider retention or individual legal rights.
Original DN instrument · version 1.0.0
DN Bank Consent and Revocation Record
Compare a stated task with requested authority, then keep future data access, payment, recurring mandate and retained-copy states separate. UK-oriented educational record; no account connection.
Enter your assumptions or load a labelled example. Required blank numbers stay missing; unknown evidence remains unknown. Use nonpersonal labels only. This instrument makes no network requests and uses no persistent browser storage.
Use your own inputs
No current result. Complete inputs or load an illustrative example.
User-entered UK-oriented evidence only. No account connection, regulated-status verification, live scope test, bank instruction, refund, deletion, legal advice or guarantee. API-version examples are not generic connector semantics; data and payment rights require the actual account and applicable documents.
1. Identify the service and legal entity behind the connection
The FCA’s provider guidance defines AIS around consolidated payment-account information and PIS around initiating an order from an account held at another provider. An AI front end, a technical connector, the regulated service and the bank can be separate participants. Name each role before judging what the permission screen means.
Ask which entity provides AIS or PIS, which activities its authorization or registration covers, and which customer-facing application will receive the result. A software vendor saying it “uses open banking” is not a substitute for that mapping. Check the relevant firm record and the specific service, rather than only searching for a recognizable trading name.
The local tool records the provider evidence as documented, mismatched or unknown. A documented input is your assertion that a reference exists. DN has not independently verified the provider for your account, and the tool does not turn a brand name into authorization.
2. Translate the task into specific data fields
TrueLayer’s Data API v1 scope documentation separates account details, balances, transactions and identity information. It also lists data-reading scopes for direct debits and standing orders. The name of a payment-related data object should not be mistaken for permission to create or change that payment.
For a monthly spending explanation, write down the smallest information set that answers the question. Does the agent need raw merchant descriptions, or will categorized totals do? Does it need every account, or a selected account? Does it need an ongoing feed, or a single statement period? These are original design questions, not a claim that every provider offers identical field-level controls.
A useful consent record pairs each requested category with its purpose and recipient. If the interface bundles more data than the task requires, ask whether the scope can be narrowed. If it cannot, make that tradeoff explicit before consenting rather than describing the connection as minimally privileged.
3. Distinguish recurring data access from a one-time read
The same TrueLayer v1 page distinguishes a short-lived access token from the offline_access permission that can return a refresh token. Consent and bank authentication are related but separate elements in its connection model. Those are version-specific documented semantics; they are not a universal claim about every bank connector.
The operational question is how the agent will get the next batch of data after the current session ends. Record the consent’s duration, any reconfirmation requirement and the mechanism that can refresh access. Do not treat a model chat ending or a temporary token expiring as evidence that every future access path has ended.
The article intentionally avoids a universal day-count rule. The provider, bank, geography and API version determine which renewal model applies. When an application upgrades its connector, compare the actual consent lifecycle rather than assuming that a field with the same name still has the same meaning.
4. Separate one payment from permission for future payments
Open Banking’s public FAQ describes variable recurring payments as a consented arrangement with parameters such as amount, frequency and duration. That is different from granting permission for one particular payment. It does not establish availability of every commercial VRP use case at every bank.
For a task to pay one invoice, ask why a recurring mandate is requested. For a recurring task, identify the beneficiary, maximum amount, frequency or period limits, end condition and the process for changing those parameters. A per-payment ceiling alone cannot answer how much may be paid across a month.
The DN tool compares the stated task with the entered scope. It flags recurring authority for a single-payment task and any payment authority for an information-only task. That is a scope-review prompt, not a finding that the provider acted unlawfully or that a customer should never choose a broader service.
5. Map the recipients beyond the bank and connector
The FCA consumer guidance says the AIS user should understand how information is used and whether it is shared. For an agent workflow, extend the practical record to the application, model service, automation platform and logs that actually receive data. A connector’s privacy statement cannot answer every downstream recipient’s practices.
Create a simple map: bank data enters the connector; selected fields enter the app; a subset may enter the model; outputs and diagnostics may be retained elsewhere. For each step, record the service, purpose, data categories and retention reference. Do not assume that a masked account number makes the rest of a transaction history anonymous.
Keep banking credentials and live tokens out of prompts, examples and exported research records. If a provider supports different authentication flows, inspect the actual flow in use. This guide does not make a blanket claim that every implementation routes credentials identically or that a “read-only” badge is independently enforced.
6. Confirm withdrawal of future data access
TrueLayer’s consumer revocation guidance identifies withdrawal through the regulated app or website, or through the bank or building society. A request is still different from evidence of its outcome. Record the affected consent, the requested action and the confirmation that applies to that consent.
For an operator, a useful offboarding test asks whether the particular connection remains capable of fetching new account data through its documented path. Do that only within an authorized test environment or support process; this article does not perform a bank query. Preserve the observation time and distinguish a cached response from newly fetched information.
Do not close the whole incident record when this one task is complete. A payment created earlier, an active recurring mandate and a copied transaction file are separate objects. The tool can therefore show data access withdrawn while those other states remain active or unresolved.
7. Resolve payment and mandate outcomes independently
TrueLayer’s Payments API v3 cancellation documentation makes the distinction concrete: a cancellation request can be accepted for processing without cancellation succeeding. Its UK flow has a state boundary after which the payment cannot be cancelled through that action. The documented result notifications, rather than the request alone, establish the API outcome.
A recurring mandate has its own lifecycle. The mandate-revocation documentation says revocation removes the ability to make new payments using that mandate, while its information remains retrievable. That statement should not be turned into a claim that all earlier payment instructions were cancelled or refunded.
Record the payment reference and outcome separately from the mandate reference and outcome. An executed payment needs its appropriate refund, dispute or recovery process; a data disconnect does not supply one. For an unrecognized or suspected unauthorized payment, contact the bank promptly using its official route. This article does not determine liability or initiate cancellation.
8. Ask what happens to copies and required records
The ICO’s public erasure guidance explains that deletion rights depend on circumstances and can be limited by obligations such as financial recordkeeping or legal claims. Its current page also says the guidance is under review after the Data (Use and Access) Act. A connection being revoked is therefore not evidence that all copies have been erased.
As a named provider example, the privacy notice on TrueLayer’s public user-terms page describes a general seven-year retention period after last service use, with circumstances that may extend retention. That is a published policy statement, not evidence that every data category or downstream merchant uses the same period. The page identifies UK and EEA entities but also includes an EEA-residence condition; it is not used here to certify UK onboarding eligibility.
Ask each recipient which data has been deleted, which categories remain, why they remain and when they will be reviewed or removed. Keep a deletion request, a response and confirmed scoped erasure as different statuses. The resulting packet makes an honest handover possible: access stopped, payment state checked, mandate addressed, and retained copies explained or still open.
Methodology, limitations and corrections
The original method is a separation of objects and task boundaries. A request to explain account information is compared with the presence of payment authority; a one-time payment task is compared with recurring authority. These are editorial prompts to reconsider scope, not automatic grant or refusal decisions. Existing consents, payments and mandates can coexist, so the tool does not reject that legitimate combination.
The instrument counts unresolved classifications and four possible pending follow-up states: data withdrawal, payment outcome, mandate revocation and erasure. Neither count measures security or legal compliance. Confirmed means recorded by the user for the identified scope. It does not mean the tool has authenticated the confirmation or inspected every copy.
Primary sources were checked on 13 November 2026. TrueLayer Data API v1 and Payments API v3 are named explicitly to prevent mixing versions. No live consent screen, bank account, production permission or provider registration for an AI application was tested. The privacy example is not an onboarding recommendation. Recheck the actual provider, bank, jurisdiction and updated ICO guidance for a real implementation.
For corrections, identify the claim, source and date when contacting Decentralised News. A new record-creation timestamp does not refresh its underlying evidence.
Change log: version 1.0.0, 2026-11-14. Initial documentation review, original instrument and labelled examples.
Frequently asked questions
Does a read-only account connection let an agent make payments?
Do not infer payment authority from account-information access. Identify the actual service and scopes, then verify the implementation. A label in an app is not an independent enforcement test, and a separate payment consent may exist alongside the data connection.
Is permission to read standing orders permission to change them?
Not in the named TrueLayer Data API v1 scope example. The documented scope concerns access to information. A different operation would need its own documented authority and supported endpoint; the shared terminology is not enough.
If I disconnect the agent, will a payment already sent be cancelled?
The payment needs its own status and process. A data-consent withdrawal does not establish cancellation. The named payment API also distinguishes a cancellation request from its final outcome.
Does revoking a recurring mandate delete the mandate record?
The named TrueLayer documentation says information about a revoked mandate remains retrievable. Future-payment authority and record retention are separate questions. This is a provider-specific example, not a universal database rule.
Must every copy of my data disappear when I withdraw consent?
Ask the relevant organizations for their specific erasure and retention response. The applicable lawful basis, legal obligations and records can matter. The tool records a pending request separately from confirmed deletion and never certifies that all copies are gone.
Does this article approve TrueLayer or an AI app for my UK account?
No. TrueLayer provides the named documentation examples. Actual production access, the correct regional terms, the regulated service, bank support and the app’s downstream data handling all need their own review.
Primary sources
- FCA: Account information and payment initiation services. Consumer consent, service roles, data-sharing information and checking the firm/activity permissions. Reviewed 2026-11-13.
- FCA: Regulations for third-party payment providers. Definitions of AIS and PIS under the UK payment-services framework. Reviewed 2026-11-13.
- TrueLayer: General Data API concepts — v1. Version-specific data scopes, offline access and distinction between consent/authentication; no universal version or day-count rule. Reviewed 2026-11-13.
- Open Banking: FAQs. Consent and parameters for variable recurring payments; no universal bank/product availability inference. Reviewed 2026-11-13.
- TrueLayer: Revoke data access or withdraw payment consent. Customer-facing app/provider/bank routes for consent withdrawal. Reviewed 2026-11-13.
- TrueLayer: Cancel a payment — Payments API v3. UK payment-state cancellation boundary and distinction between accepted request and final cancellation outcome. Reviewed 2026-11-13.
- TrueLayer: Revoke a payment mandate. Removal of new-payment ability through the mandate and continued retrieval of mandate information. Reviewed 2026-11-13.
- TrueLayer: User Terms and Consumer Privacy Notice. Published retention example and entity/regional wording; not used to certify UK onboarding eligibility. Reviewed 2026-11-13.
- ICO: Your right to get your data deleted. Conditional erasure rights, recordkeeping/legal-claim exceptions and the current guidance-review notice. Reviewed 2026-11-13.
Turn the finding into a decision
Before buying an agent connector or automation plan, request the actual consent screens, supported bank/region list, data recipients and offboarding procedure for your intended task. Use this record to compare the answers and preserve unresolved questions. No banking connector is recommended or linked through an affiliate programme here; documentation examples do not establish suitability.
Related DN research
Disclosure: Analysis and instrument results are editorial. Where labelled affiliate links appear, DN may receive compensation when you sign up or buy through them. Commercial relationships do not determine findings. No tested integration or guaranteed outcome is implied.



