What Matters
The biggest mistake in AI-agent ROI models is treating governance as a free add-on. Approval gates, audit logs, exception review, model monitoring, access controls and compliance testing consume time and money—but skipping them can make an apparently profitable automation unsafe or unusable. DN’s Compliance-Adjusted ROI Calculator turns those controls into explicit economic inputs instead of hiding them below the line.
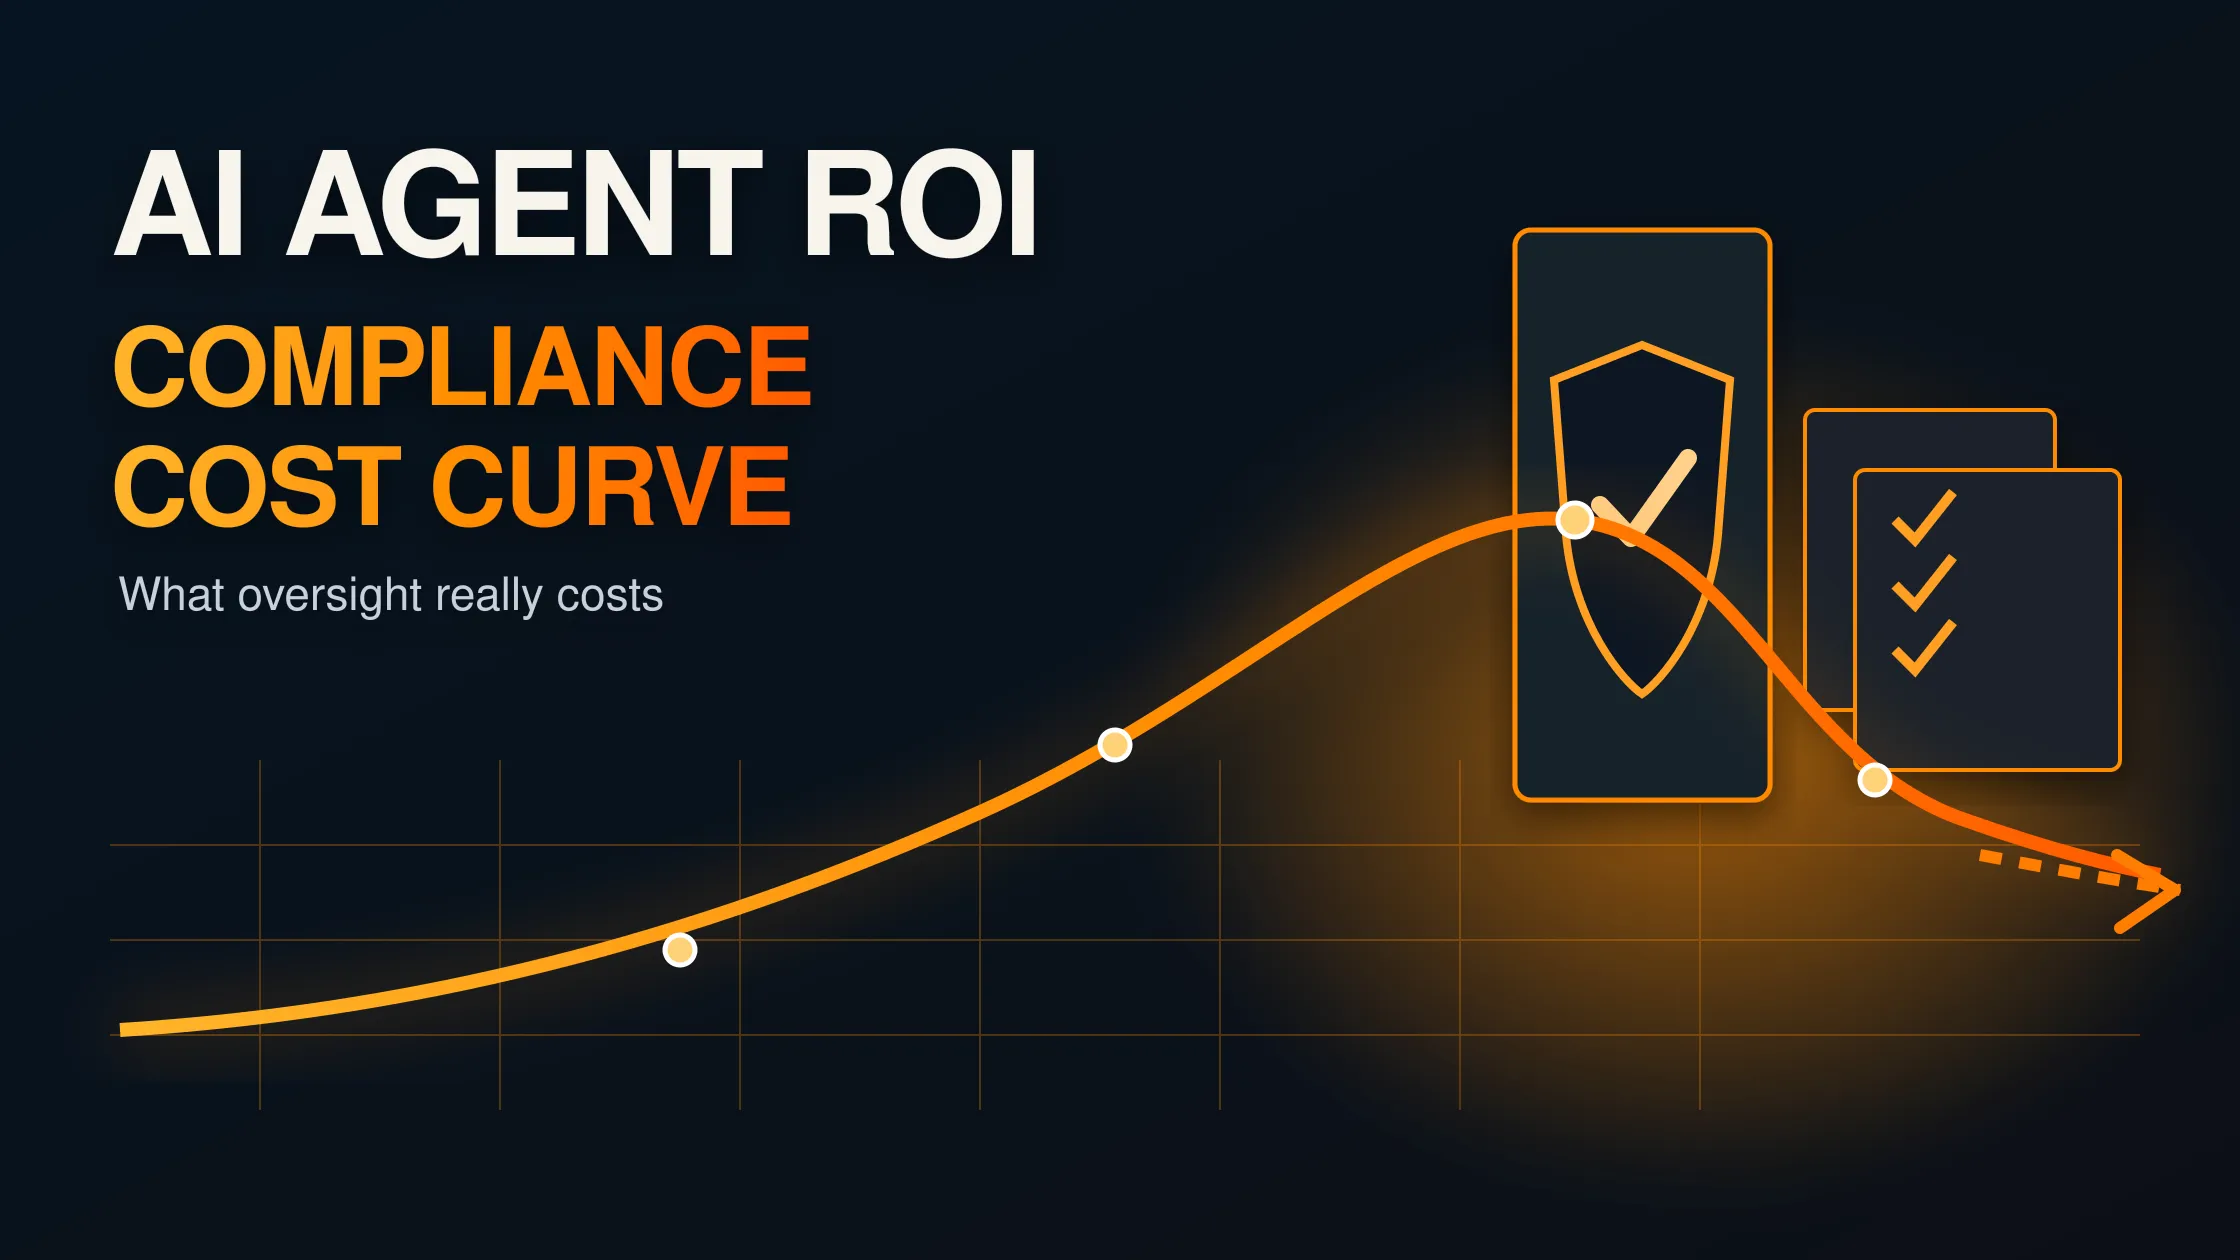
The compliance cost curve is part of agent ROI
Agentic software is often sold on a simple equation: automate more tasks, reduce labour, increase throughput. That equation is incomplete. The more consequential an autonomous action becomes, the more an organisation may need to spend on permissions, approvals, evidence retention, monitoring, escalation and independent review.
The European Commission’s current AI Act guidance makes that distinction concrete. Certain high-risk systems face requirements around risk management, documentation, logging, human oversight, robustness and monitoring, while deployers must assign human oversight and monitor relevant systems. Transparency obligations under Article 50 started applying on 2 August 2026, while the Commission’s current timeline places Annex III high-risk rules from 2 December 2027 and product-integrated high-risk rules from 2 August 2028. The exact obligations depend on classification and use case, so businesses should obtain qualified legal advice rather than infer compliance from this calculator.
NIST’s AI Risk Management Framework is voluntary rather than a law, but it reinforces a similar operating idea: AI risk management must be governed, mapped, measured and managed across the lifecycle. OWASP’s AI Agent Security guidance is even more operational, recommending least privilege, human-in-the-loop controls for high-risk actions, monitoring, structured logs and separation of decision-making from irreversible execution.
Why the cheapest agent is not always the cheapest system
| Control | Economic cost | Why it exists | Failure if omitted |
|---|---|---|---|
| Human approval gates | Reviewer minutes, queue latency | Stop high-impact actions before execution | Wrong payment, deletion, trade, account action or policy breach |
| Structured logs | Storage, engineering, review | Trace what the agent saw, decided and did | No reliable reconstruction of an incident |
| Access controls | Identity, policy and integration work | Limit tools, data and actions | Excessive agency and privilege escalation |
| Monitoring | Telemetry, alerting, analyst time | Detect drift, anomalies and repeated failures | Silent degradation or runaway actions |
| Periodic audit/testing | Assurance and red-team cost | Check controls remain effective after changes | Old approvals masking new failure modes |
| Exception review | Specialist labour | Resolve uncertain or high-risk cases | Automation of cases that should have stopped |
Compliance-Adjusted ROI Calculator
Use this model to compare the gross automation case with the cost of the control layer. Defaults are an illustrative scenario, not an industry benchmark.
The curve has three zones
1. Low-consequence automation
For reversible, low-impact work—drafting, summarisation, categorisation or internal research—the control layer can be light. Review may be sampled rather than universal, permissions can be narrow, and failures are usually recoverable.
2. Bounded operational agency
When agents update customer records, create support actions, trigger procurement steps or prepare financial workflows, economic value can still be strong, but the system needs explicit permission boundaries, exception routing, logs and post-action monitoring.
3. High-impact or irreversible execution
Payments, privileged access, employment decisions, regulated workflows and other consequential actions can require stronger human oversight and assurance. At this point, the organisation is no longer buying “an agent”; it is operating a controlled socio-technical system. The control cost can overwhelm the original automation case if the task is low-volume or low-value.
A better deployment question: where should autonomy stop?
The right target is not maximum autonomy. It is the level of autonomy that preserves enough economic value after the cost of safe operation. An agent that automates 90% of a workflow but forces expensive review of the remaining 10% may still be highly attractive. Conversely, automating 99% of a low-value process can be a poor investment if the required audit and monitoring stack costs more than the labour saved.
How to compare agent architectures economically
| Architecture | Likely control burden | Economic advantage | Watch for |
|---|---|---|---|
| Read-only assistant | Low | Fast deployment, low reversal risk | Data leakage, hallucinated recommendations |
| Proposal agent | Low–medium | Automates preparation while humans approve | Approval fatigue and rubber-stamping |
| Bounded execution agent | Medium | Strong throughput gains inside defined limits | Permission creep, weak exception routing |
| High-impact autonomous executor | High | Potentially large labour and latency savings | Assurance cost, legal exposure, irreversible errors |
Methodology and limitations
Version 1.0 treats compliance cost as an explicit layer of the agent business case. Human-review cost is calculated as annual volume × review rate × review minutes ÷ 60 × loaded hourly cost. Annual control cost adds review, logging/monitoring, audit/assurance and governance/access-control inputs. Recurring cost adds software/model expense. Compliance-adjusted annual value equals gross benefit minus recurring cost. Year-one ROI then subtracts the one-time implementation cost and divides the remaining year-one value by total year-one cost.
This model does not price legal liability, fines, reputational harm, cyber incidents, model drift or the probability of a control failure. It does not classify an AI system under the EU AI Act or certify conformity with ISO, NIST or OWASP guidance. Organisations should replace the defaults with their own costs, risk classification and qualified legal or assurance advice.
Primary sources
- European Commission — AI Act overview and implementation timeline
- European Commission — obligations for providers and deployers of high-risk AI systems
- NIST — Artificial Intelligence Risk Management Framework
- OWASP — AI Agent Security Cheat Sheet
- ISO/IEC 42001 — AI management systems
- ISO/IEC 42105 — guidance for human oversight of AI systems
FAQ
Does AI compliance always reduce ROI?
No. Controls add direct cost, but they can also prevent losses, improve reliability and make a deployment usable in workflows that would otherwise be too risky. This calculator deliberately shows the visible control cost without pretending to quantify avoided incidents.
What is compliance-adjusted ROI?
DN uses the term for an ROI calculation that includes the recurring cost of human review, logging, monitoring, assurance and governance instead of counting only software and implementation expense.
Does this calculator determine EU AI Act compliance?
No. Legal classification depends on the specific system, use case, role and jurisdiction. The calculator is an economic planning tool, not legal advice or a conformity assessment.
Should every agent have a human approval step?
No. Approval should be risk-based. Read-only or easily reversible tasks may need lighter controls, while high-impact or irreversible actions usually justify stronger human oversight and execution boundaries.
Disclosure: Decentralised News may use commercial relationships elsewhere on the site. This article does not rank vendors and contains no paid placement. Corrections: use the DN contact page and identify the article title and evidence requiring review.